Security
What is built, what is verified, and what is not done yet.
There is no badge on this page. There is a list of controls you can ask us to show you working, and a list of things we have not done.
There is no such thing as HIPAA certification
No government body certifies software as HIPAA compliant, and there is no certificate to hold. A vendor that shows you a HIPAA badge is showing you its own drawing.
What HIPAA asks of a company like ours is a business associate agreement with each practice, and safeguards that actually exist. So this page lists the safeguards, says how each one is checked, and says plainly what is still to do.
What is built and verified
Eight things that are true today. Ask, and we will show you any of them working.
The privacy policy says what we hold, why and for how long, and where: in the United States, encrypted in transit and at rest.
On the record, in words
Every visit keeps its own history: who booked it, moved it, confirmed it or cancelled it, and when. A member of staff appears by name. A patient acting from their own link appears as the patient. The phone agent appears as the phone agent.
A way out that needs no account
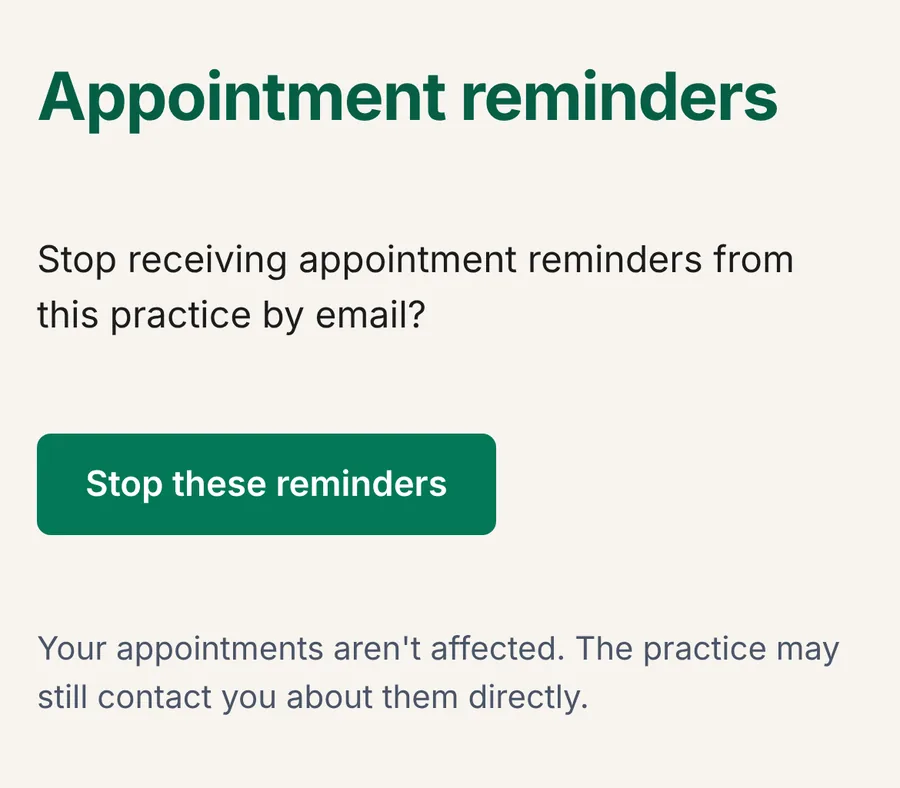
The link at the foot of a reminder opens a page with one button. Nothing happens until the patient presses it, so a mail scanner that follows the link cannot unsubscribe anyone by looking.
What we have not done
Three things a careful buyer should know before the first call.
We have no customers to show you. You would be among the first. There are no testimonials on this website because there is nobody to quote, and we would rather leave the space empty than fill it with invented praise.
Our business associate agreement has not been through a lawyer yet. It is written. Counsel reviews it before the first practice signs, and no practice puts real patient information into Ellery without a signed one.
No outside firm has audited us. There is no SOC 2 report and no third-party attestation of any kind. What is on this page is what we have built and tested ourselves.
Common questions
Is Ellery Health HIPAA certified?
No, and neither is anyone else. There is no HIPAA certification body and no certificate to hold. Ellery signs a business associate agreement with the practice and publishes the specific controls behind it on this page.
Will you sign a business associate agreement?
Yes, and before any patient information goes in. We act as your business associate, and the agreement governs how we handle protected health information.
Where is our data kept?
In the United States, encrypted in transit and at rest, with each practice's data separated from every other practice's by the database itself.
What happens to our data if we leave?
You can export it while your account is active. After the account closes we delete the practice's data, patient records included, within 30 days. Audit records, and the record of what we billed you, are kept longer because we are required to retain them.
What happens if there is a breach?
We notify the affected practice without undue delay and cooperate with the notifications it is required to make.
Do you use our patients' information for anything else?
No. Not to advertise, not to train models, and not for any purpose other than delivering the service to your practice. We never sell or rent anyone's information.
Talk to us
Book a 20-minute look. Tell us how many providers you have and what your front desk spends its day on. We will show you the app with a sample practice and answer what you ask.
- support@elleryhealth.net
- Phone
- (732) 444-7364
- Hours
- Monday to Friday, 9:00 am to 5:00 pm Eastern